Human control systems are vital to prevent automated risk mitigation failures, ensuring that autonomous actions align with business intent. While algorithms process complex telemetry at scale, human agency in tech provides the essential ethical oversight, contextual reasoning, and accountability required to navigate unpredictable operational environments safely.
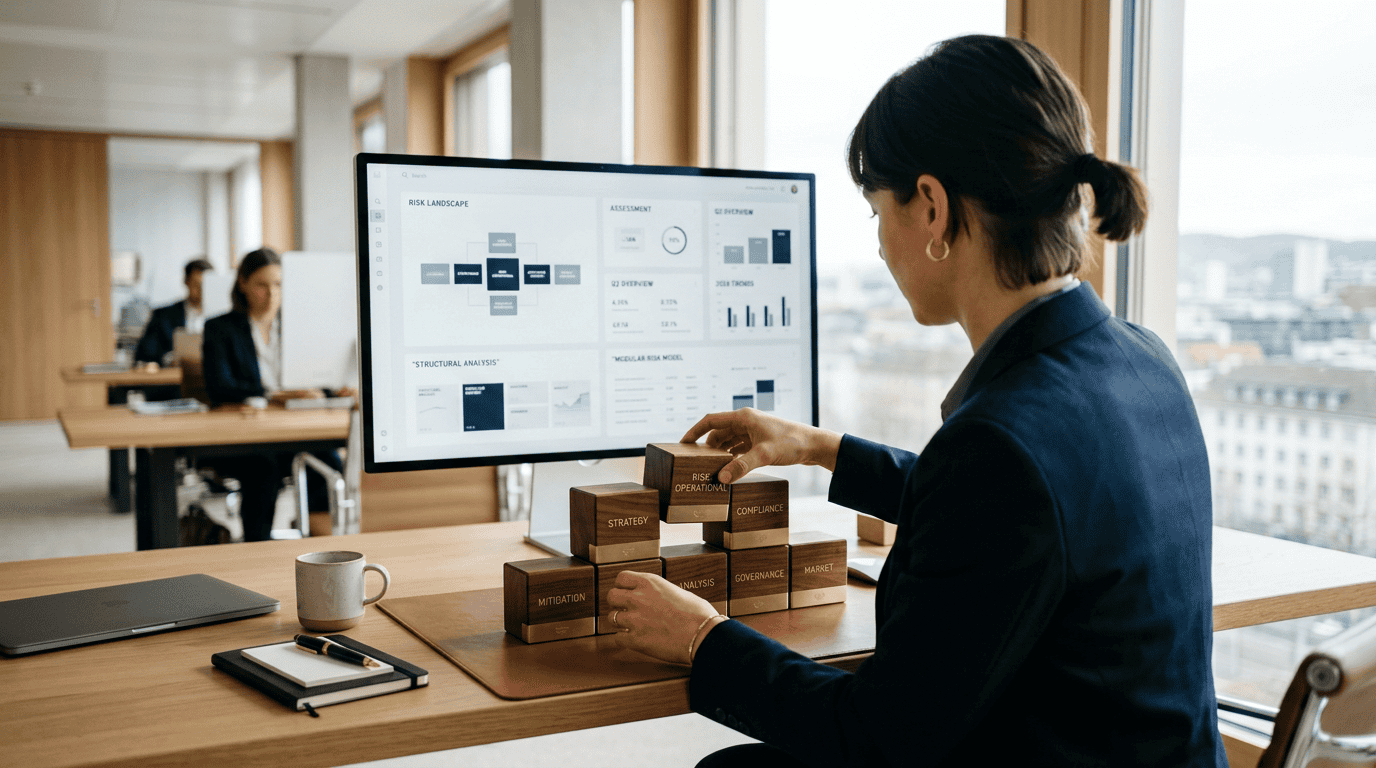
Establishing Robust Human Control Systems
As organizations increasingly deploy automated systems to manage cybersecurity, compliance, and operational tasks, the limits of pure automation have become glaringly apparent. Without dedicated human control systems, algorithmic decision-making can systematically amplify errors, leading to compounding failures that escape automated detection.
Preventing Overreliance and Algorithmic Bias
Overreliance on automation—often termed automation bias—occurs when human operators assume that an algorithmic system is inherently correct. In high-stakes environments, this passive acceptance can lead to catastrophic oversights. Maintaining a strict human-in-the-loop protocol ensures that automated outputs are treated as recommendations rather than absolute truths. This active verification layer allows human professionals to inject contextual reasoning, identifying anomalies that statistical models might overlook.
Preserving Organizational Accountability
While modern web agents can automate complex risk-scoring, threat-hunting, and compliance monitoring, they cannot assume legal or operational responsibility. Accountability remains a uniquely human attribute. Establishing clear lines of authority ensures that when automated systems trigger a mitigation action, a human operator remains responsible for validating that the response aligns with organizational policies, regulatory frameworks, and broader business goals.
The Dual Impact of AI on Human Agency in Tech
The integration of artificial intelligence into the modern workspace does not automatically diminish human capability; rather, its impact on human agency in tech is dual-sided, depending heavily on system design and organizational culture.
Factors Diminishing Human Autonomy
When automated systems are designed as closed boxes, they can significantly lower an individual’s sense of agency. This alienation typically stems from three key factors:
- Exclusion from the Loop: Employees feel sidelined when systems execute critical actions without providing visibility or override capabilities.
- Expertise Anxiety: Workers may experience anxiety that highly complex models “know better” than they do, leading them to defer to flawed machine decisions.
- Compressed Decision Windows: The machine-speed execution of modern software pressures human teams to make split-second decisions with less time for critical reflection.
Factors Elevating Professional Agency
Conversely, when AI is positioned as a collaborative partner, it can substantially elevate human agency. Systems that expose clear User Permissions and configuration options allow employees to actively direct, challenge, and shape AI strategies. Using AI as an interactive sounding board fosters self-directed learning, enabling professionals to run complex scenarios, validate hypotheses, and expand their technical capabilities without losing control over the final execution.
The Evolution of Human Risk Management
Traditional security awareness training is rapidly evolving into dynamic, telemetry-driven Human Risk Management (HRM). Rather than relying on static, annual compliance presentations, modern organizations leverage real-time data to identify and mitigate risky behaviors as they happen.
From Awareness to Real-Time Behavioral Telemetry
By monitoring user interactions across cloud applications, databases, and development environments, HRM systems collect rich behavioral telemetry. When a user exhibits a high-risk behavior—such as attempting to upload unencrypted proprietary code to a public database—the system does not merely block the action; it triggers a personalized, real-time intervention. This immediate feedback loop educates the user in the flow of work, transforming potential security incidents into measurable learning opportunities.
Connecting Risk Scores to Dynamic Access Control
Advanced HRM programs connect individual risk scoring directly to identity, access, and response workflows. For instance, if an operator’s risk profile spikes due to repeated policy violations, the system can dynamically adjust their access levels, enforce multi-factor authentication, or route their actions through a secondary review queue. This granular approach, supported by structured Smart Data governance, ensures that security teams can proactively isolate risks before they escalate into full-scale breaches.
Governing AI Agents as Non-Human Risks
The rapid proliferation of semi-autonomous AI tools introduces a novel vector: non-human risk. Unlike traditional software, which executes static, predictable scripts, AI agents operate with a degree of probabilistic autonomy, creating unique challenges for corporate governance.
The Challenge of Machine-Speed Decision Paths
AI agents execute workflows across multiple APIs, databases, and external networks at machine speed. Because they operate without the familiar physical or behavioral cues of human intent, detecting anomalous or malicious behavior requires continuous, automated monitoring. If an agent misinterprets its instructions, it can execute hundreds of erroneous transactions or content updates before a human administrator notices the divergence.
Establishing Non-Human Identity Governance
To mitigate this risk, organizations must treat active AI agents as non-human identities. This requires establishing strict guardrails, including:
- Unique Cryptographic Identifiers: Every active agent must possess a verifiable digital identity to trace its actions across the ecosystem.
- Granular API Permissions: Restricting agent access to only the specific data repositories and tools required for their designated tasks.
- Continuous Behavioral Baseline Auditing: Monitoring agent outputs against historical performance baselines to quickly flag and halt anomalous decision paths.
Adopting Structured AI Governance Frameworks
To responsibly navigate the complexities of automated risk mitigation, enterprises are increasingly adopting structured frameworks, such as the National Institute of Standards and Technology (NIST) AI Risk Management Framework (AI RMF). These frameworks provide a systematic, repeatable methodology to identify, assess, monitor, and mitigate AI-related risks throughout the system lifecycle, ensuring that human agency in tech remains the central pillar of any automated strategy.
A 5-Step Framework for AI Governance
Choose Your Platform Mode
Start free with the local Core Framework or unlock cloud AI Web Agents to automate your digital operations.
Core Mode
Offline-capable building engine for WordPress developers, freelancers, and agencies.
Smart Cloud
Connect your website to the CTS Cloud to unlock vector storage, reCAPTCHA, and Smart Data.
Web Agents
Unlock autonomous AI Web Agents to drive visitor interactions, content publishing, and sales.